Free course · Cybersecurity
SOC Analyst Level 1 with Splunk
Train for a Level 1 SOC analyst role: what the job is really like, the incident response process, the Windows event IDs you read every shift, Splunk search and SPL, hunting through Boss of the SOC v1, Wireshark traffic analysis, phishing email analysis, and MITRE ATT&CK with free threat intelligence.
Free to learn. Verifiable certificate £19 when you pass the final exam (optional, VAT included).
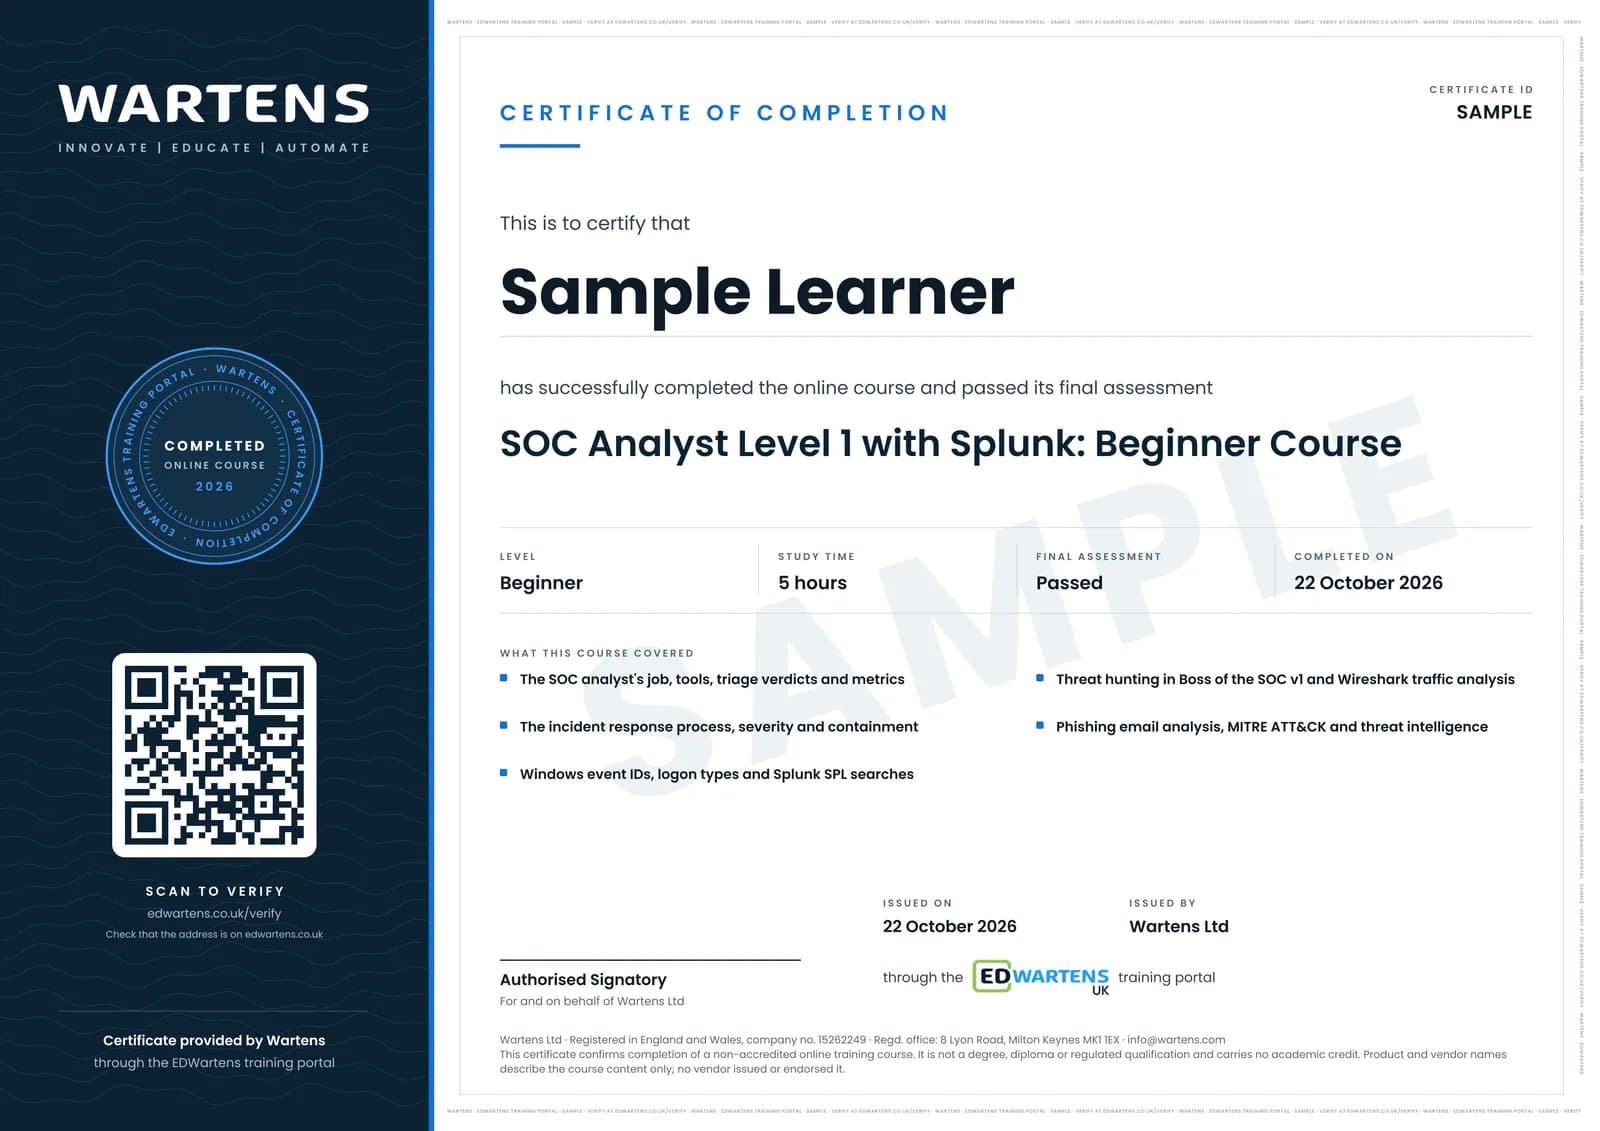
Sample certificate. Optional, issued when you pass the final exam.
- Level
- Beginner
- Modules
- 9
- Video
- 8 hours
- Price
- Free
Outcome
What you will be able to do
Describe the SOC analyst's job, tools and metrics; follow the incident response process from triage to lessons learned; read Windows logon, account and process events and spot a brute-force-to-persistence sequence; write SPL searches that count, filter and chart; hunt through the Boss of the SOC v1 dataset from a hypothesis; analyse suspicious traffic in Wireshark; analyse a phishing email from its headers, links and attachments; and map an incident to MITRE ATT&CK and check indicators against threat intelligence.
- Describe the SOC analyst's job, tools, verdicts and metrics
- Follow the incident response process and contain without losing evidence
- Read Windows logon, account and process event IDs
- Write SPL searches that filter, count and chart
- Hunt through Boss of the SOC v1 from a hypothesis
- Analyse suspicious traffic in Wireshark
- Analyse phishing emails from headers, links and attachments
- Map incidents to MITRE ATT&CK and use free threat intelligence
Software
Splunk Enterprise (the free 60-day trial, which can convert to the free licence), the public Boss of the SOC v1 dataset, Wireshark, and a Windows virtual machine for Event Viewer. All free.
Hardware
A laptop or desktop with 16 GB of RAM is comfortable for Splunk and a Windows VM together; 8 GB works if you run them one at a time.
Syllabus
9 modules
Each module has video lessons, notes and a short quiz. The final exam closes the course.
- What a SOC analyst actually does2 lessons
- The incident response process2 lessonsLab
- Windows event logs every analyst must read3 lessonsLab
- Splunk search basics and SPL3 lessons
- Hunting in Splunk: Boss of the SOC2 lessons
- Network traffic with Wireshark2 lessons
- Phishing email analysis2 lessons
- MITRE ATT&CK and threat intelligence4 lessons
- Final Assessment1 lesson
How it works
How this course works
- Watch the video lessonsOne module at a time, at your own pace.
- Take the module quizA short quiz at the end of each module shows what stuck.
- Keep your notesWrite in My notes beside each module and ask the trainer if you are stuck.
- Practise in the labOptionalTry a task from the module in the EDWartens Lab, in your browser.
- Sit the final examPass it once you have been through the modules.
- Certificate, if you want oneOptionalPaid, and only after you pass. Anyone can check it online.
EDWartens Lab
Practise this in the EDWartens Lab
Practise the judgement of a SOC shift in the OT security lab: telling normal from suspicious in a day's logs, and running a response in the right order. Splunk itself is not part of the lab.
Works alongside SOC Analyst Level 1 with Splunk. The Lab is ot security practice in your browser: no install, no hardware, free to use. Sign in as a learner and it opens with your account.
Levels to try with this course
OTS-05 · OT security lab
Spot the intruder: the events that matter in a day's log
Open in the lab (opens in a new tab)OTS-08 · OT security lab
Incident drill: a simulated note on an operator screen
Open in the lab (opens in a new tab)
Optional. Skip it whenever you like: it never blocks your progress or your certificate.
Why practise in a lab
Technical work is judged on what you can do: wiring, commissioning, finding a fault. Doing a task yourself teaches more than watching it a second time, and a lab lets you try it safely before you meet real equipment. It does not replace working on real hardware.
- Practise safely, so a mistake costs nothing.
- The lab checks your work like a site test, so you know when it is right.
- Free, in your browser, with nothing to install.
Certificate
An optional certificate when you pass
Learning is free. Pass the final exam and you can have a certificate for £19, including VAT, with a number employers can check online. It records that you completed a free online course; it is not a regulated qualification or a CPD certificate.
- Your name, the course, its study time and your final exam score
- A unique certificate number and a QR code to its verification page
- Issued by Wartens Ltd; add it to your LinkedIn profile in one click
- Pay now or after you pass: it is issued the moment you pass the final
Credits
Who made the lessons
The video lessons belong to their creators. EDWartens wrote the study plan, notes, quizzes and the final exam.
- MyDFIR
lessons on Wireshark for SOC analysts, a phishing email analysis lab, and using MITRE ATT&CK as a beginner
- ZeroDayVault (Cyber Panchayat)
lessons on the tools used in real SOC jobs, free threat intelligence websites, and beginner SOC projects
- Cyber Shield
ten Windows event IDs every SOC analyst should know
- CyberPlatter
the incident response lifecycle and NIST SP 800-61
- Hoplite Security
a Boss of the SOC v1 threat hunting walkthrough
- IBM Technology
the anatomy of an attack
- Infosec Wizard
Windows logon events 4624, 4625 and 4634
- Jon Good
using Windows Event Viewer for a security audit
- Micahs0day
a Splunk BOTSv1 APT scenario walkthrough
- Mike Chapple
the CertMike explainer on the incident response process
- Mohd Maaz
SPL commands explained
- Simply Cyber (Gerald Auger)
malicious traffic analysis in Wireshark
- Splunk How-To
basic searching in Splunk Enterprise
- SplunkGuru
an introduction to the Search Processing Language
- Tech with Jono
a real day in the life of a remote SOC analyst
- iMentor
phishing email analysis for SOC analysts
- The MITRE Corporation
the introduction to the MITRE ATT&CK framework
Questions
About this course
Do I need to know cybersecurity already?
Is this a Splunk certification course?
Do I have to pay for Splunk?
Can I do the labs on a work laptop?
Is the course really free?
What certificate do I get?
How long does the course take?
What is the project?
Want a live class and career support?
The Professional Module is five live days of Siemens PLC, HMI and SCADA with an instructor, then a resume session and a CPD certificate.