Free course · Cybersecurity
OT Network Monitoring: Zeek, Suricata and Malcolm
Passive network security monitoring for industrial plants with free tools: where to tap, reading Modbus, S7comm, EtherNet/IP, DNP3 and BACnet in Wireshark, Zeek with the CISA ICSNPP parsers, Suricata rules for OT, Malcolm and Security Onion, asset inventory from traffic, baselines, MITRE ATT&CK for ICS detections and alert triage with plant operations.
Free to learn. Verifiable certificate £19 when you pass the final exam (optional, VAT included).
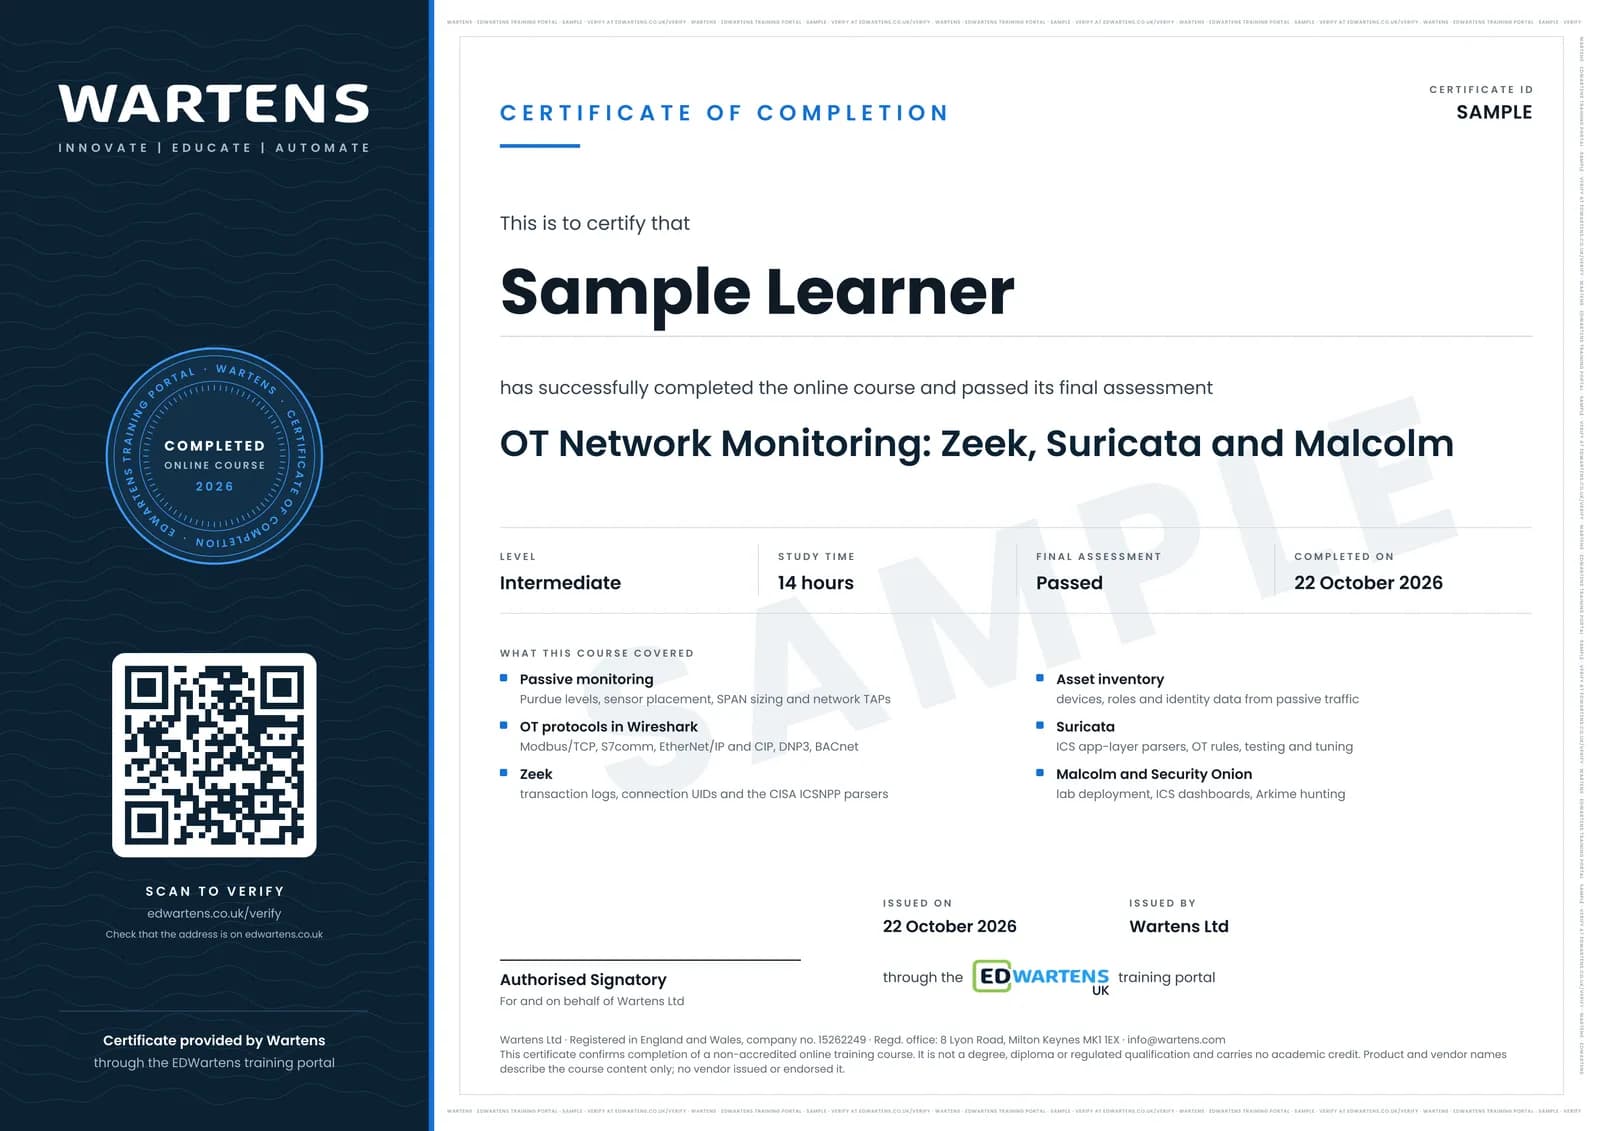
Sample certificate. Optional, issued when you pass the final exam.
- Level
- Intermediate
- Modules
- 15
- Video
- 21 hours
- Price
- Free
Outcome
What you will be able to do
Explain why passive monitoring is the safe first control in OT; place a sensor using SPAN or a TAP and size it; decode Modbus/TCP, S7comm, EtherNet/IP, DNP3 and BACnet in Wireshark; run Zeek with ICSNPP and answer questions from its logs; build an asset inventory from traffic; write and test Suricata rules for OT protocols; deploy Malcolm in a lab and hunt in its dashboards and Arkime; baseline normal traffic; map detections to MITRE ATT&CK for ICS; and triage an alert with operations and write the incident note.
- Place a passive sensor by Purdue level and size a SPAN port, or choose a TAP
- Read Modbus/TCP, S7comm, EtherNet/IP, DNP3 and BACnet traffic in Wireshark and spot writes and program transfers
- Run Zeek with CISA's ICSNPP parsers and answer operational questions from its logs
- Build an OT asset inventory from passive traffic, with evidence for every role
- Write and test Suricata rules for OT protocols, and tune them without losing the alert
- Deploy Malcolm in a lab and hunt with its ICS dashboards and Arkime
- Baseline normal OT traffic and map detections to MITRE ATT&CK for ICS
- Triage an OT alert with the control room and write a clear incident note
Software
All free: Wireshark 4.6, Zeek 9.0 with the CISA ICSNPP parsers, Suricata 8.0, Malcolm (CISA) and optionally Security Onion 3, on Linux virtual machines. Public ICS capture files stand in for a live plant.
Hardware
A computer able to run Linux virtual machines. The Wireshark, Zeek and Suricata modules run on a laptop with 8 GB of RAM; Malcolm's published minimum is a host with 8 CPU cores and 24 GB of RAM.
Syllabus
15 modules
Each module has video lessons, notes and a short quiz. The final exam closes the course.
- Why passive monitoring is the first OT security control3 lessons
- Where to tap: Purdue levels, SPAN ports and network TAPs3 lessonsLab
- Wireshark for OT traffic: capture files, filters and conversations3 lessons
- Modbus/TCP and S7comm on the wire4 lessons
- EtherNet/IP and CIP, DNP3 and BACnet on the wire3 lessons
- Zeek fundamentals: logs, UIDs and reading a capture3 lessons
- Zeek for ICS: the CISA ICSNPP parsers3 lessons
- Asset inventory from passive traffic2 lessonsLab
- Suricata for OT: rules, ICS keywords and tuning4 lessons
- Malcolm in a lab: deploy, ingest and capture5 lessons
- Hunting in Malcolm and Security Onion: dashboards, Arkime and threat intelligence5 lessons
- Baselines and anomaly detection that operators can live with3 lessonsLab
- Detection engineering with MITRE ATT&CK for ICS2 lessons
- Alert triage, escalation with operations and the incident note4 lessonsLab
- Final Assessment1 lesson
How it works
How this course works
- Watch the video lessonsOne module at a time, at your own pace.
- Take the module quizA short quiz at the end of each module shows what stuck.
- Keep your notesWrite in My notes beside each module and ask the trainer if you are stuck.
- Practise in the labOptionalTry a task from the module in the EDWartens Lab, in your browser.
- Sit the final examPass it once you have been through the modules.
- Certificate, if you want oneOptionalPaid, and only after you pass. Anyone can check it online.
EDWartens Lab
Practise this in the EDWartens Lab
Map a plant network, find the odd device and set deny-by-default firewall rules in the Lab's OT security simulator.
Works alongside OT Network Monitoring: Zeek, Suricata and Malcolm. The Lab is ot security practice in your browser: no install, no hardware, free to use. Sign in as a learner and it opens with your account.
Levels to try with this course
OTS-01 · OT security lab
Map the plant network: put every device on its level
Open in the lab (opens in a new tab)OTS-05 · OT security lab
Spot the intruder: the events that matter in a day's log
Open in the lab (opens in a new tab)OTS-08 · OT security lab
Incident drill: a simulated note on an operator screen
Open in the lab (opens in a new tab)
Optional. Skip it whenever you like: it never blocks your progress or your certificate.
Why practise in a lab
Technical work is judged on what you can do: wiring, commissioning, finding a fault. Doing a task yourself teaches more than watching it a second time, and a lab lets you try it safely before you meet real equipment. It does not replace working on real hardware.
- Practise safely, so a mistake costs nothing.
- The lab checks your work like a site test, so you know when it is right.
- Free, in your browser, with nothing to install.
Certificate
An optional certificate when you pass
Learning is free. Pass the final exam and you can have a certificate for £19, including VAT, with a number employers can check online. It records that you completed a free online course; it is not a regulated qualification or a CPD certificate.
- Your name, the course, its study time and your final exam score
- A unique certificate number and a QR code to its verification page
- Issued by Wartens Ltd; add it to your LinkedIn profile in one click
- Pay now or after you pass: it is issued the moment you pass the final
Credits
Who made the lessons
The video lessons belong to their creators. EDWartens wrote the study plan, notes, quizzes and the final exam.
- CISA
the Malcolm overviews (software, platform, configuring Malcolm and Hedgehog, live capture, dashboards, Arkime) and the webinar on foundational steps for an OT asset inventory
- Zeek
Zeek in Action lessons on the four types of monitoring data, sensor placement and new devices, Seth Grover's ZeekWeek talk on the ICS parsers, and the webinar on visualising OT networks
- OISF-Suricata
the talk on practical ICS threat hunting with Suricata
- Security Onion
Security Onion Essentials 2026 introduction and Robert Lee's talk on ICS/SCADA network security monitoring
- Malcolm Network Traffic Analysis Tool Suite
the lessons on Arkime sessions and threat intelligence feeds in Malcolm
- Dragos: OT Cybersecurity
the xOT Defense Lab episodes on passive monitoring, the do-no-harm monitoring talk and the ATT&CK for ICS webinar
- SANS ICS Security
the ICS/OT incident response lessons on detection, time-critical analysis, containment considering safety and the tabletop walkthrough
- S4 Events
the ICS ATT&CK framework talk and the panel on whether OT anomaly detection is worth it
- Chris Greer
Wireshark for beginners, filtering traffic and simple packet capture hardware
- Mike Holcomb
ICS/OT packet analysis tools
- Insane Cyber
writing Suricata rules and the basic rule format
- Keith Jones
public ICS captures for Zeek and Wireshark
- Corelight
how Suricata and Zeek work together
- HackerSploit
the introduction to Suricata IDS
- Antisyphon Training
Chris Brenton's getting started with Zeek and pcaps
- MyDFIR
a short introduction to Zeek for network analysis
- Threat Hunter's Daily
Zeek conn.log and pivoting with connection UIDs
- DEFCONConference
Norman Lundt's talk on extending Zeek for ICS defence
- ITFreeTraining
TAP and SPAN explained
- Xploit Cyber Security
Modbus packet analysis in Wireshark
- Yasin Najib
Modbus/TCP troubleshooting with Wireshark
- Markus864
setting up Wireshark to monitor PLC network traffic
- Turtle
ControlLogix EtherNet/IP and CIP traffic in Wireshark
- BrodersenSystems
DNP3 theory and a hands-on example
- Horner APG
hands-on BACnet/IP
Questions
About this course
What is OT network monitoring?
Who is this OT security monitoring course for?
Is the course free to learn, and is the software free?
Do I need a real plant or PLC to do the labs?
What hardware do I need for Zeek, Suricata and Malcolm?
How long does the course take?
Which standards and frameworks does it use?
What certificate do I get, and how is it verified?
Want a live class and career support?
The Professional Module is five live days of Siemens PLC, HMI and SCADA with an instructor, then a resume session and a CPD certificate.