
Free course · Cybersecurity
Microsoft Sentinel and Defender: SC-200 Exam Prep
Preparation for Microsoft's SC-200 Security Operations Analyst exam, mapped to the skills measured as of 21 October 2026: KQL from first query to hunting, Microsoft Defender XDR incidents and attack disruption, Defender for Endpoint, Office 365, Identity and Cloud Apps, Purview investigations, Microsoft Sentinel setup, data connectors, analytics rules, automation, Security Copilot and threat hunting.
Free to learn. Verifiable certificate £19 when you pass the final exam (optional, VAT included).
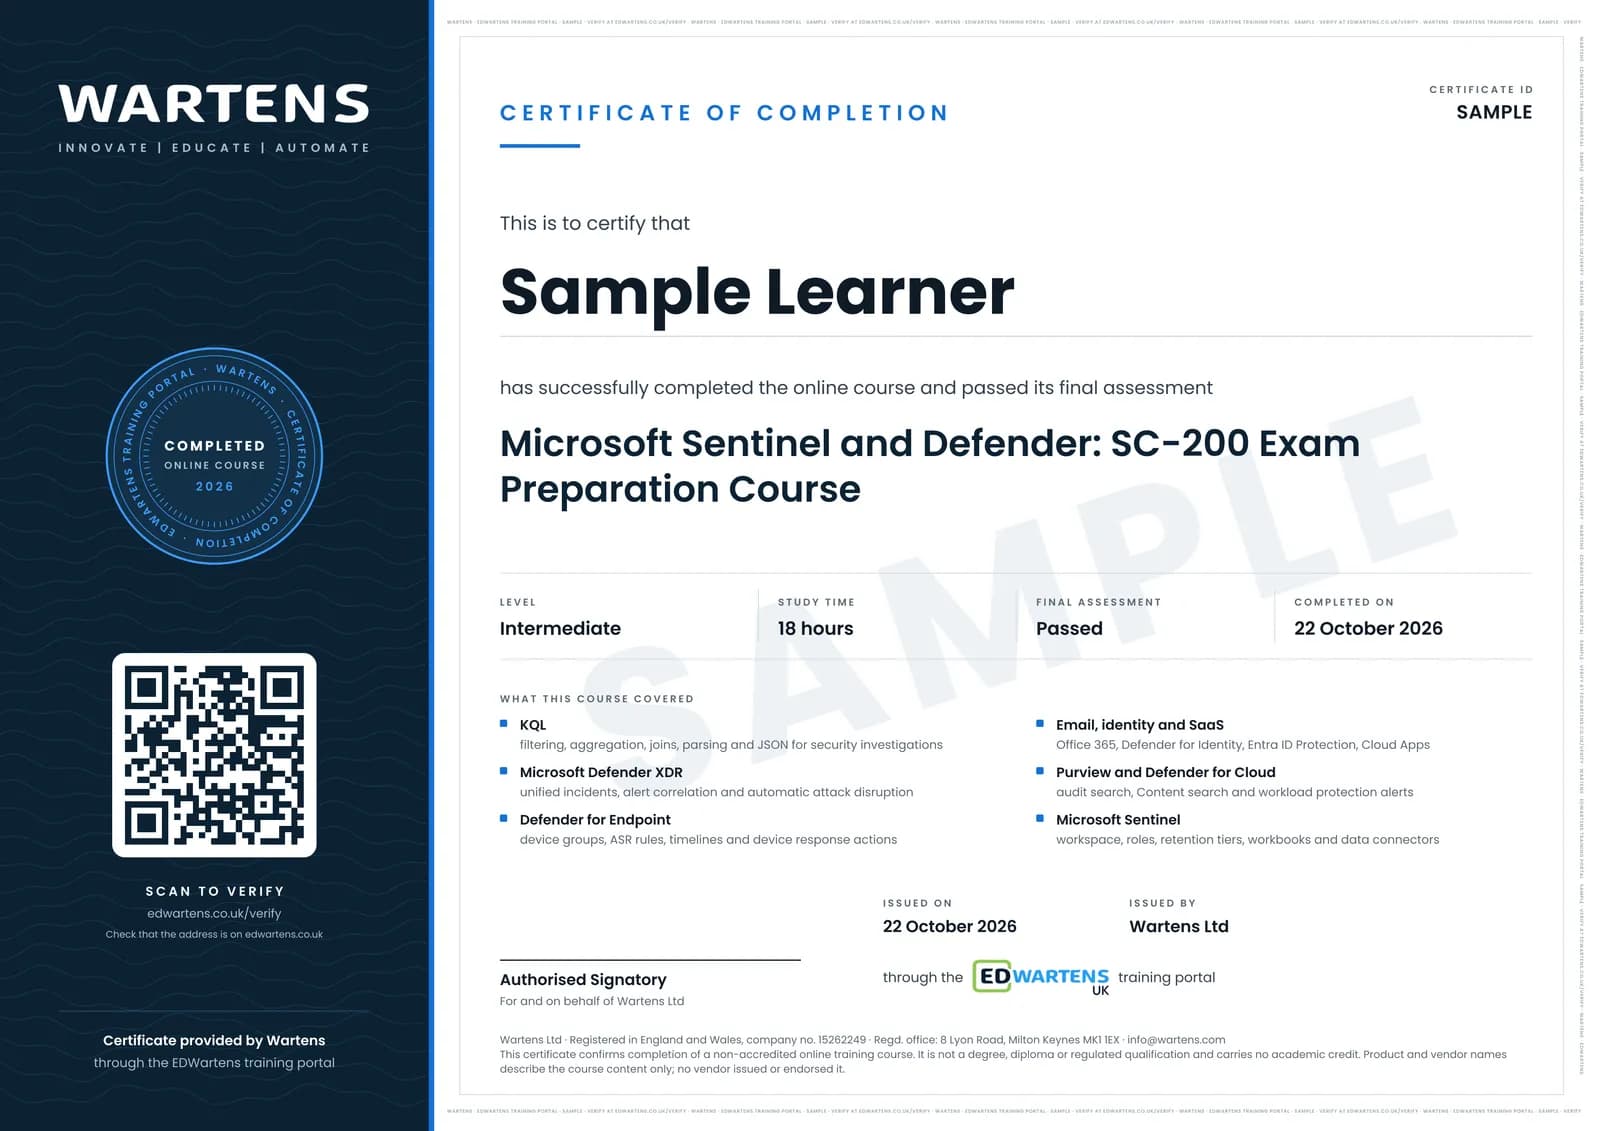
Sample certificate. Optional, issued when you pass the final exam.
- Level
- Intermediate
- Modules
- 14
- Video
- 19 hours
- Price
- Free
Outcome
What you will be able to do
Plan your SC-200 study against Microsoft's published outline; write KQL that filters, aggregates, joins and parses security data; work an incident in the Microsoft Defender portal and explain attack disruption; configure and respond with Defender for Endpoint; investigate email, identity and SaaS threats; search Purview Audit and eDiscovery; set up a Microsoft Sentinel workspace with the right roles, retention and data connectors; build analytics and custom detection rules mapped to MITRE ATT&CK; automate response with automation rules and playbooks; check Security Copilot output against evidence; and hunt with Advanced hunting, the data lake and notebooks.
- Plan SC-200 study against the three skill areas and weights Microsoft publishes
- Write KQL that filters by time, aggregates, joins tables and unpacks JSON for investigations
- Work incidents in the Microsoft Defender portal and explain automatic attack disruption
- Configure Defender for Endpoint device groups, ASR rules and response actions
- Investigate phishing, compromised identities and risky OAuth apps across Office 365, Entra and Cloud Apps
- Set up a Microsoft Sentinel workspace with least-privilege roles, sensible retention and filtered data connectors
- Build analytics and custom detection rules mapped to MITRE ATT&CK, and automate response with approval gates
- Hunt with Advanced hunting, the Sentinel data lake, KQL jobs and notebooks, and check Security Copilot output
Software
A browser and an Azure subscription you control: an Azure free account works for the Sentinel workspace, and a new workspace has a time-limited Microsoft Sentinel free trial (check the current terms on Microsoft Learn). Microsoft 365 E5 or Defender trial licences for the Defender XDR modules where available. KQL practice runs free on the Azure Data Explorer help cluster.
Hardware
A computer with a browser. A Windows virtual machine, local or in Azure, for the endpoint and log collection exercises.
Syllabus
14 modules
Each module has video lessons, notes and a short quiz. The final exam closes the course.
- The SC-200 exam, the Defender portal and a safe lab4 lessons
- KQL fundamentals for security analysts3 lessons
- KQL for investigations: let, join, union, parse and JSON4 lessons
- Microsoft Defender XDR: incidents, alerts and attack disruption5 lessons
- Microsoft Defender for Endpoint: configure, investigate and respond5 lessons
- Email, identity and SaaS threats: Office 365, Identity, Entra and Cloud Apps7 lessons
- Microsoft Purview investigations and Defender for Cloud alerts3 lessons
- Microsoft Sentinel: workspace, roles, retention and workbooks5 lessons
- Getting data into Microsoft Sentinel5 lessons
- Detections: analytics rules, custom detections and MITRE ATT&CK coverage3 lessons
- Automation: automation rules, playbooks and case management5 lessons
- Microsoft Security Copilot and agents in the SOC4 lessons
- Threat hunting: Advanced hunting, Sentinel hunting, data lake and notebooks10 lessons
- Final Assessment1 lesson
How it works
How this course works
- Watch the video lessonsOne module at a time, at your own pace.
- Take the module quizA short quiz at the end of each module shows what stuck.
- Keep your notesWrite in My notes beside each module and ask the trainer if you are stuck.
- Sit the final examPass it once you have been through the modules.
- Certificate, if you want oneOptionalPaid, and only after you pass. Anyone can check it online.
Certificate
An optional certificate when you pass
Learning is free. Pass the final exam and you can have a certificate for £19, including VAT, with a number employers can check online. It records that you completed a free online course; it is not a regulated qualification or a CPD certificate.
- Your name, the course, its study time and your final exam score
- A unique certificate number and a QR code to its verification page
- Issued by Wartens Ltd; add it to your LinkedIn profile in one click
- Pay now or after you pass: it is issued the moment you pass the final
Credits
Who made the lessons
The video lessons belong to their creators. EDWartens wrote the study plan, notes, quizzes and the final exam.
- Microsoft Learn
the official SC-200 video series: course preview, Defender XDR, Security Copilot, Purview, Defender for Endpoint, Defender for Cloud, KQL, Sentinel configuration, connecting logs, detections and threat hunting
- Microsoft Security
short product demos on Defender XDR incidents, alert correlation, attack disruption, Defender for Endpoint onboarding and settings, Office 365 investigation, Sentinel in the Defender portal, unified RBAC, SOC optimization, connectors, threat intelligence, case management, Security Copilot agents, Advanced hunting, the hunting graph, the Sentinel data lake, KQL jobs, notebooks, Sentinel graph and the MCP server
- Microsoft Mechanics
the overview of the Microsoft Sentinel platform in the first module
- Microsoft Security Community
the demo of near-real-time detection rules in Microsoft Sentinel
- Cloud360 Training
KQL basic operators and joins, Defender for Office 365, Defender for Identity, Entra ID Protection, Defender for Cloud Apps and a step-by-step Sentinel playbook
- Peter Rising
SC-200 lessons on alert and vulnerability notification rules, Defender XDR detection rules and Defender XDR automation
- CyberPlatter
collecting Windows Security events into Sentinel with the Azure Monitor Agent
- Christopher Nett
the full SC-200 study cram offered as optional revision in the final module
Questions
About this course
What is the SC-200 exam?
Who is this SC-200 preparation course for?
Is the course free to learn?
What do I need to know before I start?
How long does the SC-200 course take?
Does this course include Microsoft Security Copilot and the Sentinel data lake?
What certificate do I get, and is it the Microsoft certification?
What jobs does SC-200 preparation lead to?
Want a live class and career support?
The Professional Module is five live days of Siemens PLC, HMI and SCADA with an instructor, then a resume session and a CPD certificate.