Free course · Cybersecurity
ISO 27001:2022 Implementation: Build an ISMS
Build an information security management system to ISO/IEC 27001:2022, step by step: context, interested parties and scope, leadership and policy, risk assessment and risk treatment, the Statement of Applicability, the 93 Annex A controls in four themes, documented information and evidence, supplier, cloud, incident and continuity controls, internal audit and management review, corrective action, the stage 1 and stage 2 certification audits, and how the ISMS maps to GDPR, NIS2, SOC 2 and NIST CSF 2.0.
Free to learn. Verifiable certificate £19 when you pass the final exam (optional, VAT included).
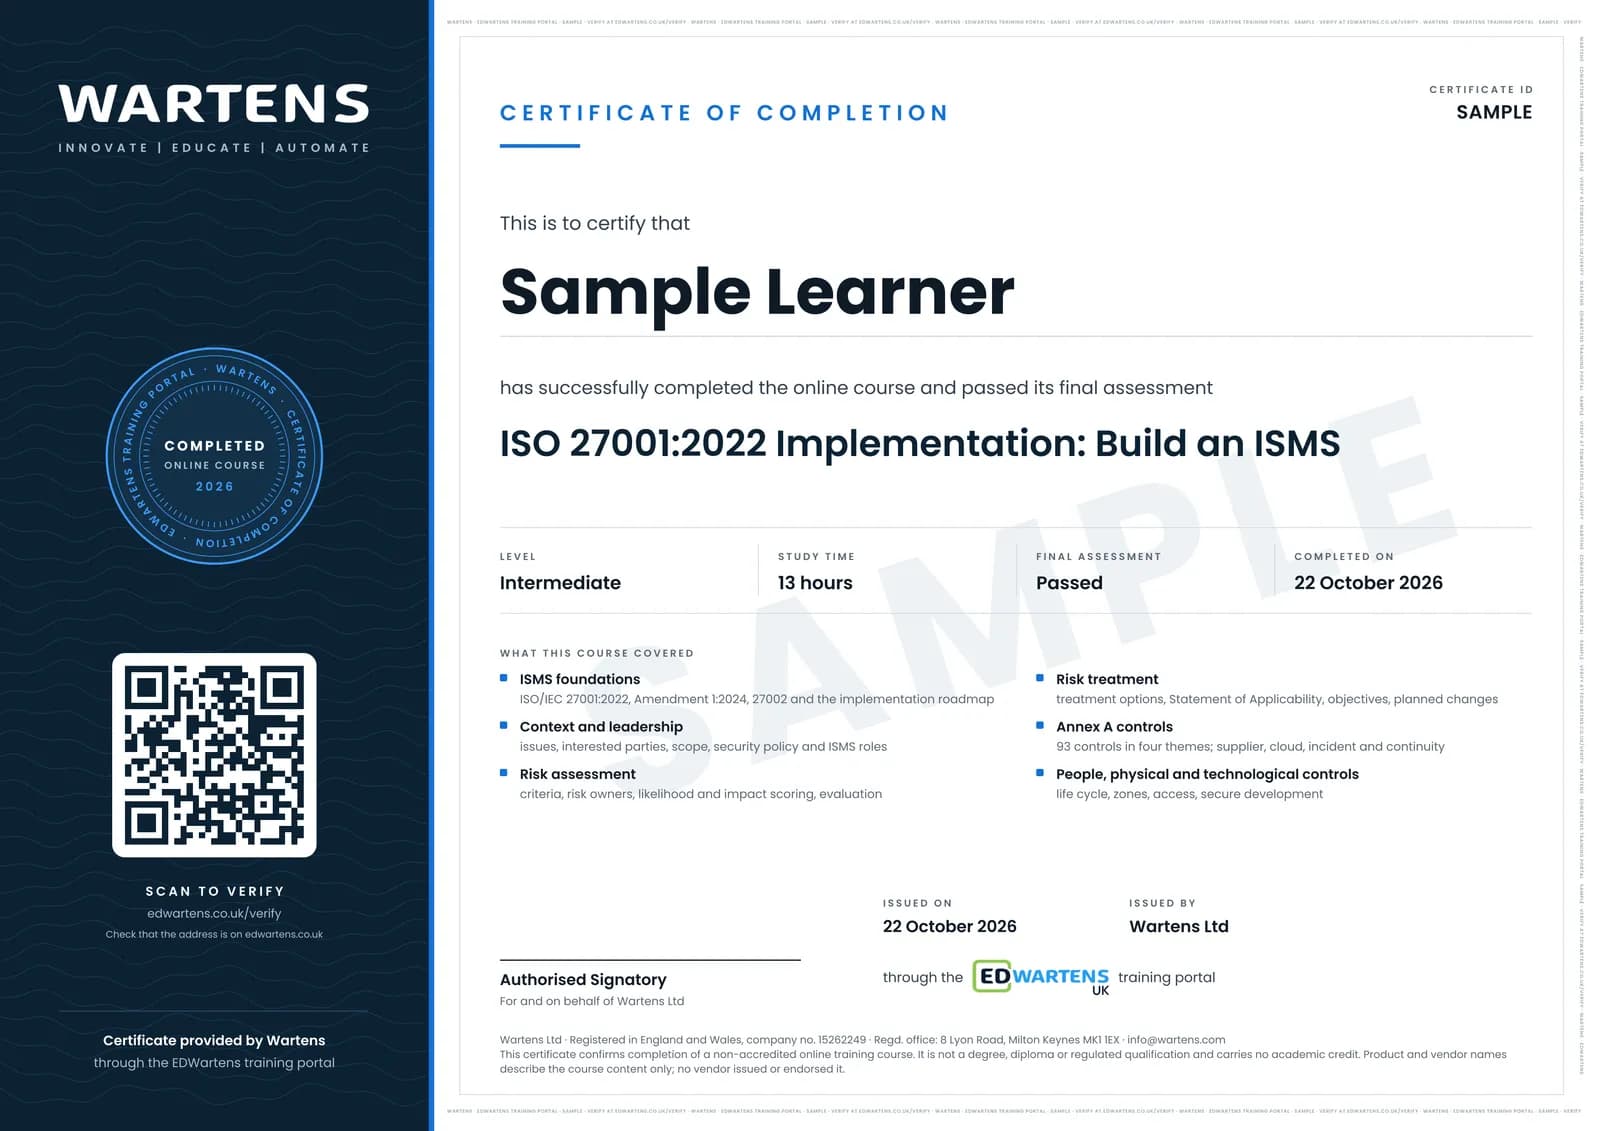
Sample certificate. Optional, issued when you pass the final exam.
- Level
- Intermediate
- Modules
- 14
- Video
- 19 hours
- Price
- Free
Outcome
What you will be able to do
Plan an ISO 27001 implementation as a project with a gap analysis; set the ISMS scope from the context, interested parties and interfaces, including the 2024 climate amendment; write an information security policy and assign roles; define risk criteria, run a risk assessment and calculate risk levels; choose treatment options and write the risk treatment plan; build a Statement of Applicability with a justification for every Annex A control; apply organisational, people, physical and technological controls; control documented information and keep the evidence an auditor samples; run an internal audit and a management review; write corrective actions from root causes; prepare for the stage 1 and stage 2 certification audits; and map the ISMS to GDPR, NIS2, SOC 2 and NIST CSF 2.0.
- Plan an ISO 27001:2022 implementation with a gap analysis and a phased roadmap
- Write the context, interested parties and a credible ISMS scope, including the 2024 climate amendment
- Set risk criteria, run a risk assessment and calculate risk levels against an acceptance threshold
- Choose risk treatments and build a Statement of Applicability that justifies every Annex A control
- Apply the 93 Annex A controls across organisational, people, physical and technological themes
- Control documented information and keep the records an auditor samples
- Run an internal audit and a management review, and write corrective actions from root causes
- Prepare for stage 1 and stage 2 certification audits and map the ISMS to GDPR, NIS2, SOC 2 and NIST CSF 2.0
Software
A spreadsheet (LibreOffice Calc or Google Sheets is free) for the risk register and the Statement of Applicability, and a document editor for policies and procedures. You do not need to buy the standard to follow the course, but anyone implementing it for real should hold a licensed copy of ISO/IEC 27001:2022 and its 2024 amendment.
Hardware
None.
Syllabus
14 modules
Each module has video lessons, notes and a short quiz. The final exam closes the course.
- ISO 27001 and the ISMS: what the standard asks for3 lessons
- The implementation roadmap: project, gap analysis and the 2022 changes3 lessons
- Clause 4: context, interested parties and the ISMS scope3 lessons
- Clause 5: leadership, the security policy and roles3 lessons
- Clause 6.1.2: risk criteria and the information security risk assessment3 lessons
- Clause 6.1.3 to 6.3: risk treatment, the SoA, objectives and planning changes3 lessons
- Annex A and ISO/IEC 27002:2022: 93 controls in four themes3 lessons
- Organisational controls: suppliers, cloud, incidents and continuity4 lessons
- People, physical and technological controls in practice3 lessons
- Clauses 7 and 8: support, documented information and operation3 lessons
- Clause 9: monitoring, internal audit and management review3 lessons
- Clause 10 and certification: corrective action and the stage 1 and stage 2 audits3 lessons
- Mapping the ISMS to GDPR, NIS2, SOC 2 and NIST CSF 2.02 lessons
- Final Assessment1 lesson
How it works
How this course works
- Watch the video lessonsOne module at a time, at your own pace.
- Take the module quizA short quiz at the end of each module shows what stuck.
- Keep your notesWrite in My notes beside each module and ask the trainer if you are stuck.
- Sit the final examPass it once you have been through the modules.
- Certificate, if you want oneOptionalPaid, and only after you pass. Anyone can check it online.
Certificate
An optional certificate when you pass
Learning is free. Pass the final exam and you can have a certificate for £19, including VAT, with a number employers can check online. It records that you completed a free online course; it is not a regulated qualification or a CPD certificate.
- Your name, the course, its study time and your final exam score
- A unique certificate number and a QR code to its verification page
- Issued by Wartens Ltd; add it to your LinkedIn profile in one click
- Pay now or after you pass: it is issued the moment you pass the final
Credits
Who made the lessons
The video lessons belong to their creators. EDWartens wrote the study plan, notes, quizzes and the final exam.
- Dejan Kosutic
the Advisera lessons on what ISO 27001 is, the clauses, the seven implementation steps, setting the scope, risk assessment and treatment, writing the Statement of Applicability, implementing Annex A controls and internal audit essentials
- Consultants Like Us
the clause-by-clause explanations of clauses 4 to 9, the information security policy and mandatory policies, the Annex A lessons on supplier relationships, cloud services, incident management planning, ICT readiness and the secure development life cycle, and preparing for the stage 1 and stage 2 audits
- Stuart Barker
ISO 27001 and ISO 27002 compared, implementing clause 4, management review, continual improvement, and the Annex A lessons on remote working and user endpoint devices
- Prabh Nair
the end-to-end implementation case study, the project initiation document, building a Statement of Applicability from scratch and writing effective ISMS documents
- URM Consulting
the guide to ISO 27001 risk assessment and the summary of the ISO 27002:2022 update
- CertiKit
the detailed walk-through of an ISO 27001 risk assessment
- NQA Certification
the certification body's webinar on understanding the ISO 27001:2022 Annex A controls
- risk3sixty
getting ready for an ISO 27001 certification audit
- SoftComply
the webinar on implementing NIS2 alongside ISO 27001
- GRC Made Simple
the key differences between ISO 27001 and SOC 2
Questions
About this course
What is the ISO 27001 implementation course?
Who is this ISO 27001 course for?
Which version of ISO 27001 does the course teach?
What is a Statement of Applicability in ISO 27001?
Is this an ISO 27001 lead implementer or lead auditor certification?
How long does the course take, and is it free?
What certificate do I get?
What jobs does ISO 27001 implementation knowledge lead to?
Want a live class and career support?
The Professional Module is five live days of Siemens PLC, HMI and SCADA with an instructor, then a resume session and a CPD certificate.