Free course · AI and machine learning
AI Security and the OWASP Top 10 for LLMs
The security course for people who have already built something with an LLM: the attack surface a model adds, all ten 2026 OWASP LLM risks one at a time, indirect injection and zero-click agent attacks, what leaks out through a chatbot, securing agents with identity and least privilege, the OWASP MCP and agentic guidance, red-teaming with MITRE ATLAS, and the NIST-based governance a plant or a GCC can actually enforce.
Free to learn. Verifiable certificate £19 when you pass the final exam (optional, VAT included).
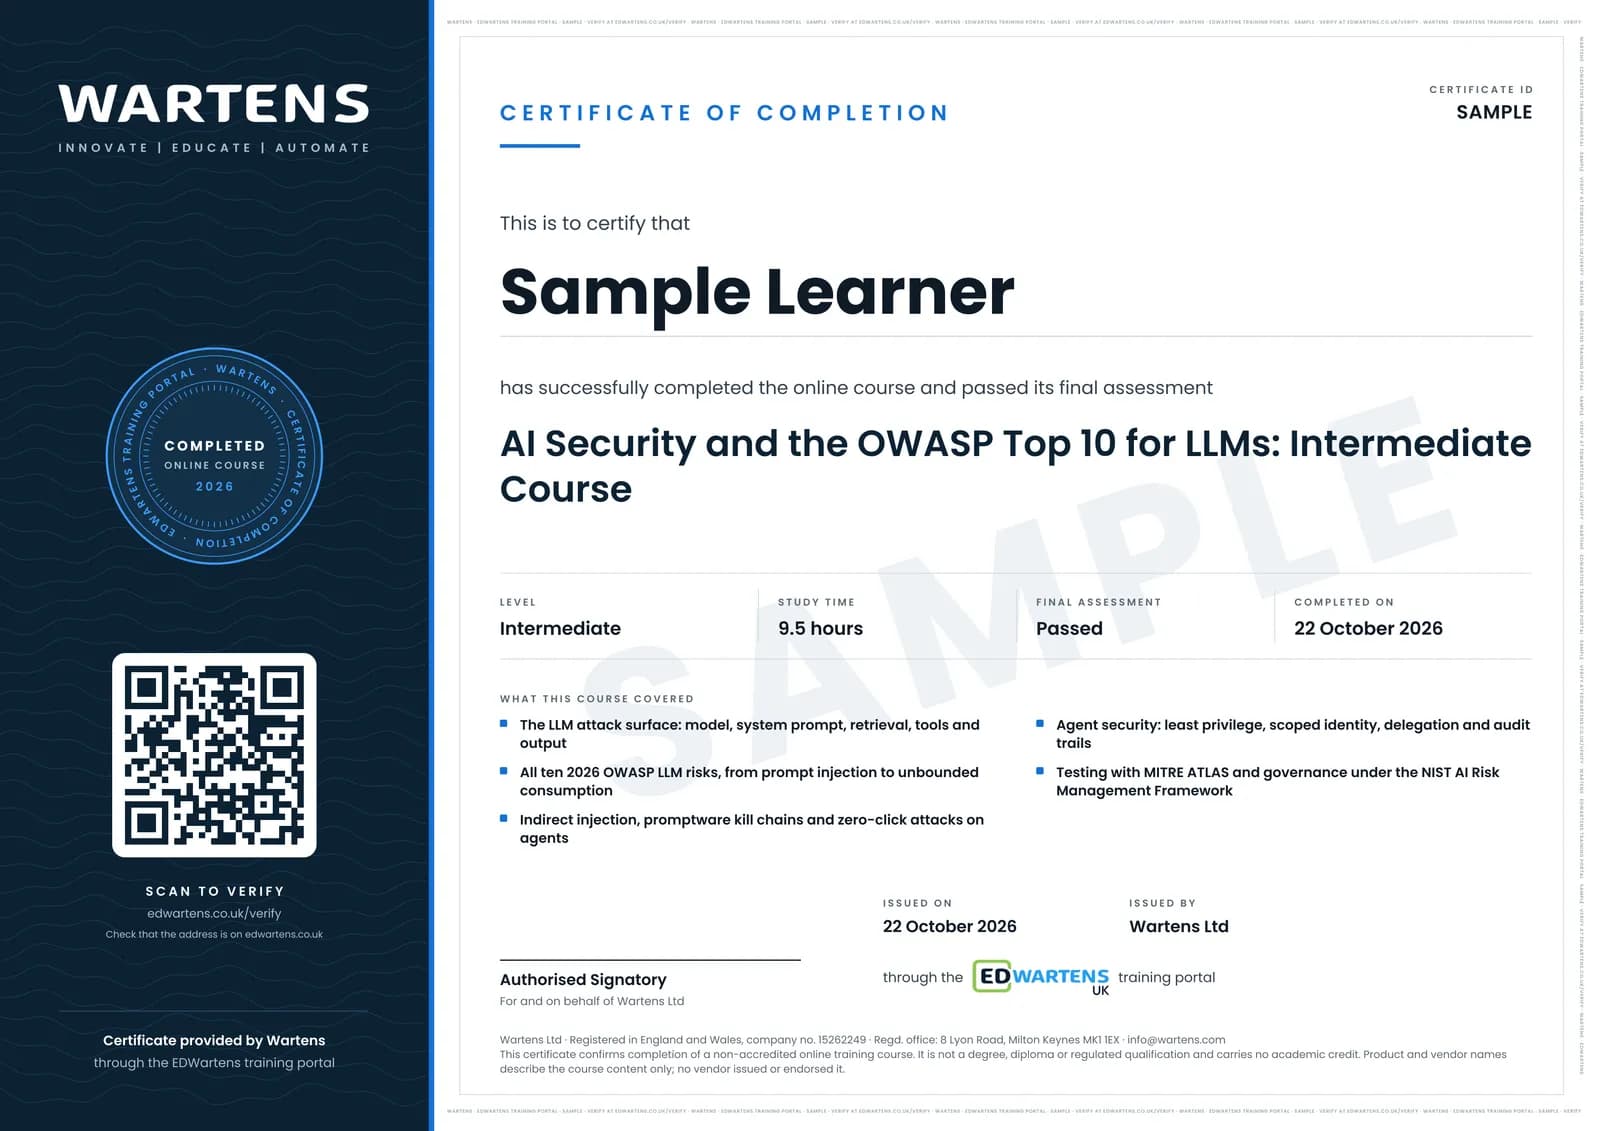
Sample certificate. Optional, issued when you pass the final exam.
- Level
- Intermediate
- Modules
- 15
- Video
- 14 hours
- Price
- Free
Outcome
What you will be able to do
Threat-model an AI feature by its parts; name and defend against all ten OWASP LLM risks; trace an indirect injection from a poisoned document to an executed action; write the rule for what may be pasted into a public chatbot; check the provenance of a model, dataset or plugin before it is used; scope an agent's tools, identity and permissions so it cannot act beyond its brief; review a connector before wiring it in; plan a pen test of an LLM feature; and fill the register entry and AI-use policy that make the whole thing auditable.
- Draw an AI feature as its parts and mark where an outsider's text can enter
- Name all ten 2026 OWASP LLM risks and sort a real incident into the right one
- Trace an indirect injection from a poisoned document to an executed action
- Write the one-page rule on what may and may not be pasted into a public chatbot
- Scope an agent's tools, identity and permissions to the least it actually needs
- Plan a pen test of an LLM feature and fill the AI register entry behind it
Software
None required. A free chatbot account is enough for the leakage and grounding exercises.
Hardware
None.
Syllabus
15 modules
Each module has video lessons, notes and a short quiz. The final exam closes the course.
- Why an LLM is a new attack surface4 lessons
- The 2026 OWASP Top 10 for LLM applications2 lessons
- LLM01: prompt injection and its defences4 lessonsLab
- Indirect injection, promptware and zero-click attacks3 lessonsLab
- LLM02 and LLM08: what leaks out4 lessonsLab
- LLM04 and LLM05: supply chain, data and model poisoning4 lessons
- LLM10 and LLM03: output handling and excessive agency4 lessonsLab
- LLM09 and LLM07: retrieval weaknesses and misinformation4 lessonsLab
- LLM06: unbounded consumption and the cost of running AI4 lessons
- Securing AI agents: architecture and zero trust4 lessons
- Agent identity, privilege and delegation3 lessons
- OWASP guidance for agentic applications and MCP2 lessons
- Testing AI systems: MITRE ATLAS, pen-testing, adversarial AI3 lessons
- Governance: NIST AI RMF and a rule people can follow4 lessons
- Final assessment0 lessons
How it works
How this course works
- Watch the video lessonsOne module at a time, at your own pace.
- Take the module quizA short quiz at the end of each module shows what stuck.
- Keep your notesWrite in My notes beside each module and ask the trainer if you are stuck.
- Practise in the labOptionalTry a task from the module in the EDWartens Lab, in your browser.
- Sit the final examPass it once you have been through the modules.
- Certificate, if you want oneOptionalPaid, and only after you pass. Anyone can check it online.
EDWartens Lab
Practise this in the EDWartens Lab
Try the defences from the course on a safe, made-up system in the AI Workbench: injection resistance, approval before action, data kept out and answers grounded in sources.
Works alongside AI Security and the OWASP Top 10 for LLMs. The Lab is ai for industry practice in your browser: no install, no hardware, free to use. Sign in as a learner and it opens with your account.
Levels to try with this course
AIW-06 · AI Workbench
Prompt to spec
Open in the lab (opens in a new tab)AIW-10 · AI Workbench
Privacy first
Open in the lab (opens in a new tab)AIW-07 · AI Workbench
Answers with sources
Open in the lab (opens in a new tab)AIW-08 · AI Workbench
A safe agent
Open in the lab (opens in a new tab)
Optional. Skip it whenever you like: it never blocks your progress or your certificate.
Why practise in a lab
Technical work is judged on what you can do: wiring, commissioning, finding a fault. Doing a task yourself teaches more than watching it a second time, and a lab lets you try it safely before you meet real equipment. It does not replace working on real hardware.
- Practise safely, so a mistake costs nothing.
- The lab checks your work like a site test, so you know when it is right.
- Free, in your browser, with nothing to install.
Certificate
An optional certificate when you pass
Learning is free. Pass the final exam and you can have a certificate for £19, including VAT, with a number employers can check online. It records that you completed a free online course; it is not a regulated qualification or a CPD certificate.
- Your name, the course, its study time and your final exam score
- A unique certificate number and a QR code to its verification page
- Issued by Wartens Ltd; add it to your LinkedIn profile in one click
- Pay now or after you pass: it is issued the moment you pass the final
Credits
Who made the lessons
The video lessons belong to their creators. EDWartens wrote the study plan, notes, quizzes and the final exam.
- IBM Technology
the attack-surface, prompt injection, promptware kill chain, zero-click, shadow AI, corpus poisoning, LLMjacking, agent security, zero trust, MITRE ATLAS and NIST AI RMF explainers
- Vandana Verma
the risk-by-risk walkthrough of LLM01 to LLM10, the first look at the OWASP MCP Top 10, and the OWASP Securing Agentic Applications guide
- Jeff Crume
the long adversarial AI session on evasion, model inversion, model theft and deepfakes
Questions
About this course
Who is it for?
What do I need to know first?
Is this the OWASP certification?
Is this a hacking course?
How long is it?
Is the course really free?
What certificate do I get?
Who made the video lessons?
Want a live class and career support?
The Professional Module is five live days of Siemens PLC, HMI and SCADA with an instructor, then a resume session and a CPD certificate.