Functional safety means that a safety function, such as an emergency stop or a guard interlock, performs correctly when it is needed, to a level of reliability matched to the risk. For machinery you choose between ISO 13849-1 (Performance Levels PL a to PL e) and IEC 62061 (Safety Integrity Levels SIL 1 to SIL 3); process plants use IEC 61511, itself an implementation of IEC 61508. For high-demand safety functions, PL e and SIL 3 both sit in the band of 10^-8 to below 10^-7 dangerous failures per hour. The older rule of thumb "SIL for process, PL for machines" is a simplification: both machinery standards are in current use, and the choice is made by the machine builder.
What is the difference between SIL and PL?
Both rate how reliably a safety function performs, but they come from different standards and use different methods. IEC 61508-1:2010 is the generic basic safety publication: it takes a risk-based approach, introduces safety integrity levels and, as the IEC says, does not itself specify the level required for any particular function. Sector standards then apply it. IEC 61511-1:2016 is the process-industry implementation for safety instrumented systems. IEC 62061:2021 is the machinery sector standard within the IEC 61508 framework; its scope is control systems for machines in high or continuous demand mode, and the IEC notes this edition extends it to non-electrical technologies and moves from "SILCL" to the "maximum SIL" of a subsystem. ISO 13849-1:2023 (fourth edition, published April 2023) specifies a methodology for the design and integration of safety-related parts of control systems of any technology, for high demand and continuous modes, and ISO says it does not specify which safety functions or required performance levels apply in a given application.
| Feature | ISO 13849-1:2023 | IEC 62061:2021 | IEC 61511 |
|---|---|---|---|
| Rating scale | PL a to PL e | SIL 1 to SIL 3 | SIL, set within the IEC 61508 framework |
| Sector | Machinery | Machinery | Process industry |
| Technology | Any (electrical, hydraulic, pneumatic, mechanical) | Electrical and, in the 2021 edition, non-electrical | Safety instrumented systems |
| Demand mode | High demand and continuous (not low demand) | High and continuous demand | Safety instrumented systems; see the standard |
| Parent standard | Refers to the IEC 61508 series for low-demand mode | Sector standard within IEC 61508 | Process sector implementation of IEC 61508 |
How do the PL and SIL numbers line up?
They line up by probability of dangerous failure per hour (PFHd). SICK's guide to performance levels lists PL a as 10^-5 up to 10^-4 per hour, PL b from 3 x 10^-6 to below 10^-5, PL d from 10^-7 to below 10^-6, and PL e from 10^-8 to below 10^-7 (PL c sits between b and d). A Siemens help document for IEC 62061 lists SIL 3 as 10^-8 to below 10^-7, SIL 2 as 10^-7 to below 10^-6, and SIL 1 as 10^-6 to below 10^-5. So, broadly, PL e matches SIL 3, PL d matches SIL 2, and PL b and PL c both fall inside the SIL 1 band. The match is on the failure-rate band only. Each standard has its own architecture, diagnostic coverage, common-cause failure and systematic-integrity requirements, so you cannot declare a PL from a SIL, or the reverse, by looking at the number.

Is functional safety a legal requirement in the UK?
Machine safety is a legal requirement; the standards are the usual way of showing you have met it. In Great Britain the Supply of Machinery (Safety) Regulations 2008 apply to supplying machinery, not the EU Machinery Directive itself. GOV.UK publishes the list of designated standards for machinery, updated most recently on 8 August 2026, and its UKCA guidance says machinery outside the higher-risk list in Schedule 2, Part 4 can be self-declared, as can machinery in that list where all relevant designated standards are applied in full and cover all applicable essential requirements. Users of machinery have duties under PUWER 1998 as well. Whether a particular edition of ISO 13849-1 or IEC 62061 is designated, and what that means for your product, needs checking against the current gov.uk consolidated list or with a conformity assessor; this is general information, not legal advice.
What does the safety lifecycle look like?
Both families follow the same logic: understand the hazard, define the function, design, verify, validate, and keep it working. In practice, for each safety function you write down:
- Hazard and risk assessment, ending in a required PL (PLr) or SIL.
- Safety requirements specification: what triggers it, what safe state it reaches, how fast.
- Architecture and component selection: sensor, logic, final element (contactor or drive), with PFHd data from the manufacturers and a calculation of the whole chain.
- Implementation: wiring, safety logic, parameters.
- Verification and validation: test the function and the failure responses against the specification.
- Operation: proof testing, inspection and controlled change. IEC 62061:2021 added requirements on periodic testing and expanded requirements on parameterisation.
Which safety functions do automation engineers meet most often?
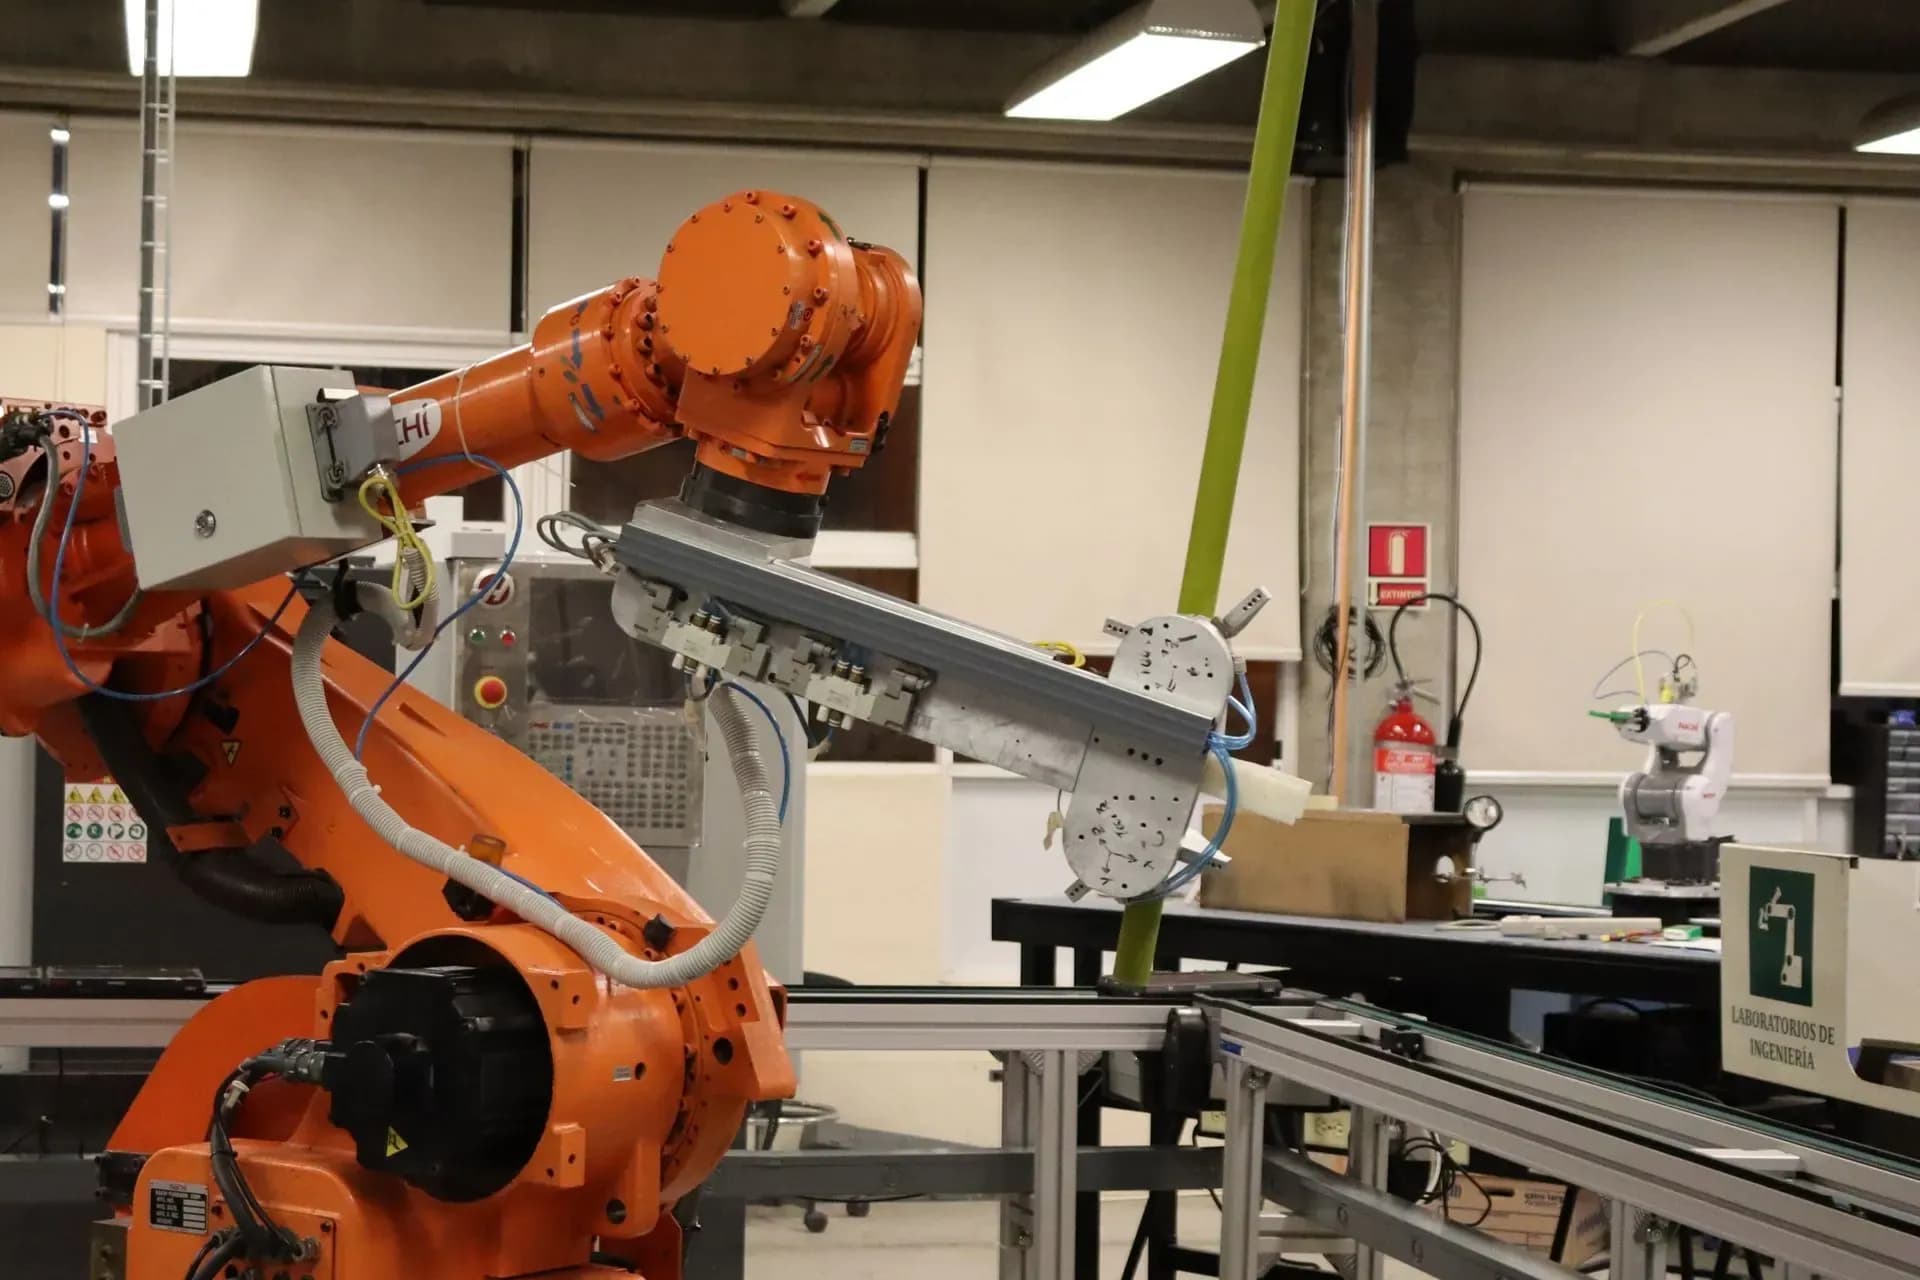
Emergency stop, guard door monitoring, light curtains and scanners, two-hand control, safe speed monitoring and safe torque off (STO) on drives are the staples. IEC 60204-1:2016 reorganised its clause on safe torque off, emergency stop and control circuit protection, so the electrical build and the safety design need to agree. For robots and cells, see our robot and PLC integration guide.
How do safety PLCs fit in?
A safety PLC runs standard and safety programs in one controller, but the safety side has extra discipline. Siemens states that all its S7-1500 and ET 200MP fail-safe I/O modules can be used in applications up to PL e / SIL 3, integrated over PROFIsafe on PROFINET or PROFIBUS. Siemens' programming guideline for S7-1200/1500 adds the working rules: the safety program has signatures that identify its state, a changed signature means the safety program has to be validated again and accepted, and changes to the safety program are reserved for users with the safety password. A passed signature check is evidence for validation, not a replacement for it, and the chosen PL or SIL still depends on the entire safety function, not the controller alone.
What does a worked safety-function example look like?
Take a guard door on a packing machine that must stop a motor when opened. The risk assessment decides how severe, how frequent and how avoidable an injury would be, and that yields a required performance level, say PL d. You then choose a door switch with safety contacts, a safety relay or fail-safe input, and a contactor pair or a drive with safe torque off, each with manufacturer PFHd or B10d data. The architecture, diagnostic coverage and common-cause measures are assessed for the chain as a whole; if the calculated PL is below the required PL, you improve the weakest element rather than arguing with the number. Finally you test the function: open the door with the machine running, check the stop time, and check what happens on a wiring fault, because the failure response is part of what you validate. Free tools such as SISTEMA are widely used for the PL calculation, and the free course linked below shows the method.
How EDWartens can help
EDWartens UK does not teach safety PLC programming or functional safety calculations. The Professional Module is a five-day live online Siemens TIA Portal class (PLC, HMI, WinCC SCADA) plus self-paced Basic Engineering, whose video modules include safety and standards. It costs £2,140 + VAT (£2,568), runs weekly from Monday with up to 10 learners, and comes with a CPD certificate recording 80 hours of learning; it is not a regulated qualification. For a free start on this topic, EDWartens' sister site offers a machine safety course covering ISO 13849 and SISTEMA. Safety design should be done by or under a competent safety engineer. You can sign up here.